Tim Grieveson explains why today’s security leaders must translate cyber threats into business language, focusing on risk, resilience, and measurable outcomes.

Tim Grieveson explains why today’s security leaders must translate cyber threats into business language, focusing on risk, resilience, and measurable outcomes.
ISO 22336 states that an organization’s top management should develop a resilience policy. This article looks at what a resilience policy should include and the steps involved in preparing one.
The Cyber Governance Code of Practice has been created to support boards and directors in governing cyber security risks.
The Enterprise Risk Management (ERM) Initiative at NC State University, in partnership with Protiviti, has released its 13th annual edition of the Executive Perspectives on Top Risks report.
Cybersecurity remains the top priority for audit committees at public companies, outside of financial reporting and internal controls, according to survey findings…
A new global survey from Splunk has found that 82% of CISOs now report directly to the CEO, a large increase from 47% in 2023. In addition, 83% participate in board meetings ‘somewhat often’ or ‘most of the time’.
PwC has published the results from its 28th Annual Global CEO Survey. Amongst other things, this shows that 42% of CEOs believe their company will not be viable beyond the next 10 years without reinvention.
The BCI has released its latest report, A Year in the World of Resilience. Here, Resilience Forward takes a look at one of the key areas highlighted in the report, the role of senior management in organizational areas related to resilience.
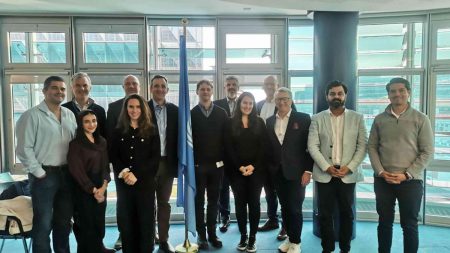
The United Nations Office for Disaster Risk Reduction (UNDRR) has announced the launch of the Network of Corporate Chief Resilience Officers (CCRO). This initiative, part of the…
The Australian Institute of Company Directors (AICD) has announced that its Cyber Security Governance Principles have been refreshed to respond to the evolving risk environment.