ISO 22336 states that an organization’s top management should develop a resilience policy. This article looks at what a resilience policy should include and the steps involved in preparing one.

ISO 22336 states that an organization’s top management should develop a resilience policy. This article looks at what a resilience policy should include and the steps involved in preparing one.
Absolute Security has published the 2025 Resilience Index, a report based on actual telemetry from over 6 million enterprise PCs. The report claims that ‘the conventional notion of resilience may already be obsolete’.
Zimperium has announced the release of its 2025 Global Mobile Threat Report, which highlights critical mobile device threat trends from the past year.
Many CISOs already oversee strong security programs focused on prevention, detection, and response. However there’s growing recognition that resilience needs to be an integral part of strategies. Tim Sherbak offers some advice for CISOs on moving forward into cyber resilience.
Nexthink has published new research exploring the challenges that IT leaders face in preparing for the next wave of AI-driven digital transformation.
A new survey-based report from Semperis looks at The State of Enterprise Cyber Crisis Readiness.
Veeam Software has published the findings of its latest research in the From Risk to Resilience: Veeam 2025 Ransomware Trends and Proactive Strategies Report.
Datadog, Inc. has released a new report, the State of DevSecOps 2025, which found that only a fraction of critical vulnerabilities really need prioritizing.
CSA has published its SaaS Security Report 2025, based on a survey commissioned by Valence Security.
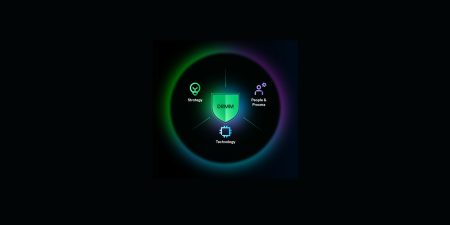
A new Data Resilience Maturity Model (DRMM) provides an empirical framework for organizations to assess their current resilience posture, identify gaps, and implement targeted improvements.