Mobile devices are increasingly being used as a method of gaining unauthorised access to enterprise networks. Nico Chiaraviglio explains how this threat area is likely to develop through 2025.

Mobile devices are increasingly being used as a method of gaining unauthorised access to enterprise networks. Nico Chiaraviglio explains how this threat area is likely to develop through 2025.
Resilience is one of those subjects that falls into the hard-to-measure category: nevertheless, there are ways and means of getting a handle on some of the key components.
In today’s digital landscape, where consumers increasingly rely on online reviews for decision-making, review bombing has emerged as a growing challenge for businesses.
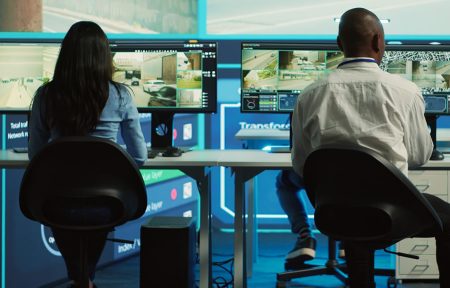
If the video server collecting your video feeds goes down, your security team is blind, and the building, the manufacturing floor, or whatever you are intent on protecting becomes vulnerable. Configuring your VMS infrastructure for high availability is key to minimizing this vulnerability.
Beyond improving security, zero trust also supports regulatory compliance by enforcing strict access controls and maintaining detailed audit trails.
With the end of the year approaching, Resilience Forward is starting to look ahead to 2025 and how the resilience profession and the challenges it faces may develop. In the first of our look-ahead articles, Bridewell cyber security experts highlight six areas where organizations will need to adapt to remain resilient in 2025…
Leadership and stewardship are at a premium in these turbulent and uncertain times; they help embed resilience. They come particularly to the fore in a crisis or disruption, but success is sown in the months and years before.
At the recent 2024 Counter Ransomware Initiative Summit 39 countries alongside international cyber insurance bodies backed new guidance which aims to support organizations experiencing ransomware attacks and to boost global resilience.
What does resilience mean for cybersecurity specifically? How can organizations prepare themselves to manage adversity and change?
In many cases, there is a significant delta between a GRC team’s perception of their organization’s maturity versus the actual reality when various requirements, priorities, and outcomes are considered, explains Matt Hillary, CISO of Drata.