Attackers are increasingly bypassing MFA not by breaking technology, but by overwhelming users. Michael Downs looks at the issue and what organizations can do to reduce risk and strengthen resilience.

Attackers are increasingly bypassing MFA not by breaking technology, but by overwhelming users. Michael Downs looks at the issue and what organizations can do to reduce risk and strengthen resilience.
Barracuda Networks has released data showing that 90% of ransomware incidents in 2025 exploited firewalls through unpatched software or a vulnerable account.
ENISA has published a Cybersecurity Exercise Methodology, which aims to ‘empower and guide organizations in developing effective cybersecurity exercises from start to finish’.
Guidance based on artificial intelligence may be uniquely placed to foster biases in humans, leading to less effective decision-making, say researchers…
Ivanti has published findings from its 2026 State of Cybersecurity Report: Bridging the Divide. Drawing on insights from more than 1,200 cyber security professionals worldwide…
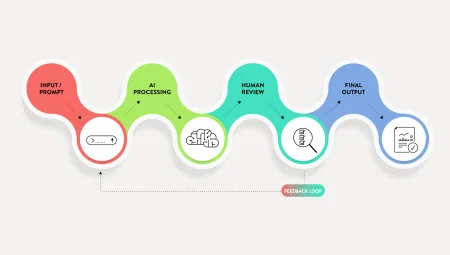
Strategic discussions about AI often centre on workforce restructuring and automation. A more immediate enterprise risk is emerging: failure to design effective human-in-the-loop (HiTL) operating models.
There are few walks of life where readiness is proven by paperwork alone. Yet when it comes to cyber security, many organizations still equate compliance filings…
Daoud Abdel Hadi examines how rising regulatory scrutiny is pushing banks and other financial institutions to embed explainability and accountability into AI-driven compliance systems.
Cloudflare has released its quarterly DDoS threat report for Q4 2025, highlighting the latest global attack trends and insights.
Airmic and BCI have released a new publication, Putting Organizational Resilience Into Practice, a jointly developed report that looks at how organizations are building, governing, and embedding resilience.