Close Menu
  • Home
  • Managing resilience
    • AI resilience
    • Business continuity
    • Business resilience
    • Climate resilience
    • C-suite and the board
    • DORA – the EU Digital Operational Resilience Act
    • Operational resilience
    • Organizational resilience
    • Supply chain resilience
    • Technology
  • Risk
    • Enterprise risk management
    • Operational risk
    • Threatscape
  • Cyber resilience
    • Cyber resilience updates
    • DORA – the EU Digital Operational Resilience Act
    • Product updates
More items
  • All News
  • Research
  • Jobs in Resilience
  • Resilience Resources
  • About Resilience Forward
X (Twitter) LinkedIn
  • Home
  • Managing resilience
    • AI resilience
    • Business continuity
    • Business resilience
    • Climate resilience
    • C-suite and the board
    • DORA – the EU Digital Operational Resilience Act
    • Operational resilience
    • Organizational resilience
    • Supply chain resilience
    • Technology
  • Risk
    • Enterprise risk management
    • Operational risk
    • Threatscape
  • Cyber resilience
    • Cyber resilience updates
    • DORA – the EU Digital Operational Resilience Act
    • Product updates
Login
LinkedIn Bluesky
Resilience Forward
Subscribe Now
  • All News
  • Research
  • Jobs in Resilience
  • Resilience Resources
  • About Resilience Forward
Resilience Forward
You are at:Home»Cyber resilience»M&S reports £300m impact of ‘highly sophisticated cyber incident’
Cyber resilience

M&S reports £300m impact of ‘highly sophisticated cyber incident’

May 21, 20254 Mins Read
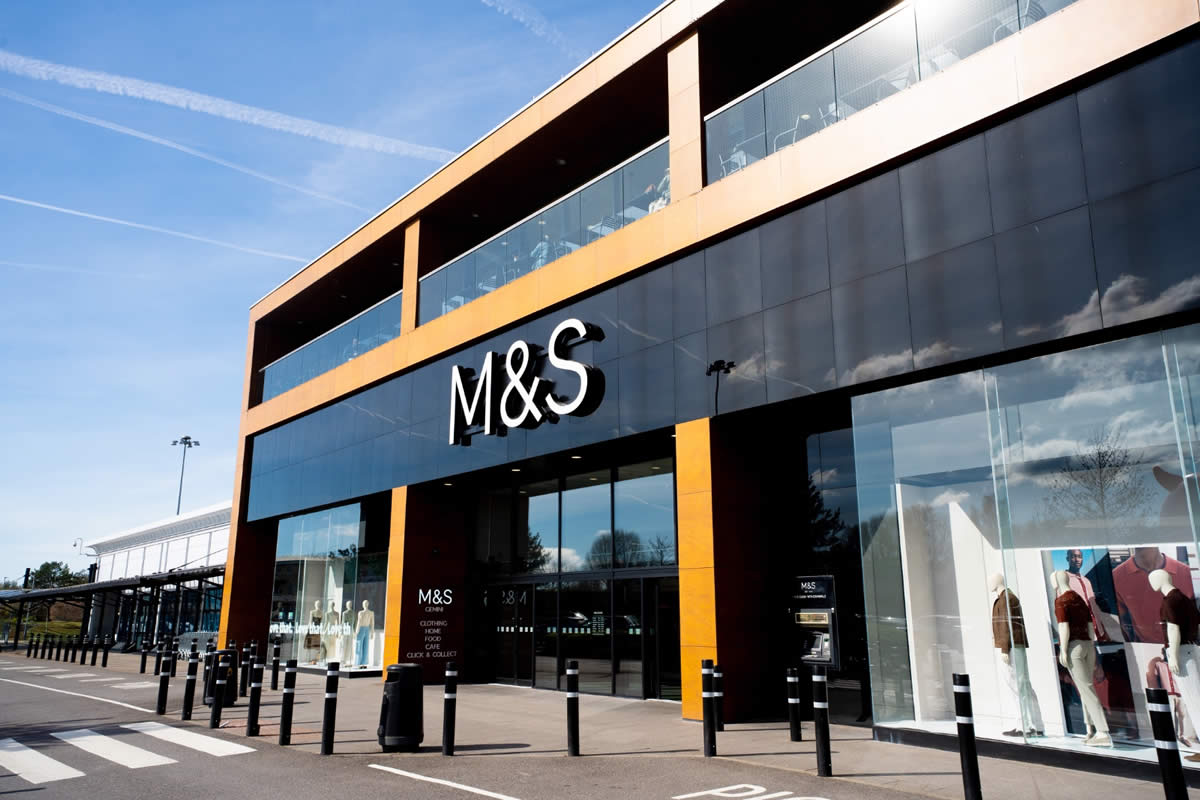
MS Gemini: source, M&S media library

Marks and Spencer Group Plc (M&S), the UK-based major retailer, has published its full year results to the end of March 2025, using the announcement to highlight that a cyber incident that started in April is expected to have a £300m financial impact on the 2025/26 operating profit.

The company says that it has tried to turn the incident into an opportunity by using the recovery process as a means to transform the technology infrastructure and to identify improved ways of working.

In the full year results media release M&S Chief Executive Stuart Machin stated:

“Over the last few weeks, we have been managing a highly sophisticated and targeted cyber-attack, which has led to a limited period of disruption. We have tackled this head on with incredible spirit, teamwork and deep sense of responsibility as we prioritised serving our customers.

“It has been challenging, but it is a moment in time, and we are now focused on recovery, with the aim of exiting this period a much stronger business. There is no change to our strategy and our longer-term plans to reshape M&S for growth and, if anything, the incident allows us to accelerate the pace of change as we draw a line and move on.

“Over the last 140 years, M&S has overcome many challenges – testament to the longevity of this brand. This incident is a bump in the road, and we will come out of this in better shape, and continue our plan to reshape M&S for customers, colleagues and shareholders.

“I would like to thank all of our colleagues and supplier partners for their hard work and dedication and, importantly thank our customers. They have been unwavering in their support, and we are incredibly grateful for their patience and trust in M&S.”

Further points given in the media release include:

  • The M&S team has worked around the clock with suppliers and partners to contain the incident and stabilise operations, taking proactive measures to minimise the disruption for customers.
  • M&S is seeking to make the most of the opportunity to accelerate the pace of improvement of its technology transformation and has found new and innovative ways of working.
  • M&S is focused on recovery, restoring its systems, operations, and customer proposition over the rest of the first half, with the aim of exiting this period a much stronger business.

Industry comments

Jason Gerrard, Senior Director of Systems Engineering at cyber resilience company, Commvault:

“This morning’s news that M&S may not fully recover from its cyber attack until July is a stark reminder of the importance of true cyber resilience. Organizations can no longer afford to simply rely on their defences to keep attackers out, they must be able to recover fast. Behind the scenes, teams are scrambling to rebuild systems, trace breach origins, and restore customer data with forensic precision – all while execs are juggling regulators, insurers, auditors and shareholders. The longer it takes to return to ‘normal’, the more that ‘normal’ drifts further away,  both in business operations and public perception. While recovery takes 24 days on average, some organizations don’t achieve business-as-usual for over 200 days, with M&S falling at the higher end of this scale. 

“This headline-grabbing downtime should be a warning to others that preparation for such a scenario is vital. Having a tried and tested recovery plan in place and identifying your minimum viable company (MVC) ahead of time can help to reduce some of the damage that can very quickly spiral out of control. Understanding your MVC – the essential systems needed to stay operational – is central to achieving cyber resilience and maintaining continuous business, even amidst a cyber attack. 

“The true power of the MVC model is not simply about responding to threats – it builds future-ready organizations that can adapt, recover, and lead, even in the most hostile conditions. In doing so, they are safeguarding their data and systems, as well as their reputation and long-term viability. If a brand as established as M&S can be brought to its knees by a cyber incident, what does that say about the average business? This is a market-wide wake-up call.”

UK
Share. Facebook Twitter Pinterest LinkedIn Tumblr Email WhatsApp
Previous ArticleISACA highlights COBIT as a tool for AI systems governance
Next Article Poor digital experiences are having large business impacts

Related Posts

A solar farm with associated wind turbines.

The resilience challenges of the renewable energy transition

October 2, 2026
Sovereign cloud concept - a digital map of the world is overlaid with multiple cloud icons of different sizes.

Sovereignty and resilience: considerations for organizational leaders

October 2, 2026
A medical worker in a hazmat suit responds to a pandemic victim.

UN pandemic meeting renews preparedness calls but fails to agree declaration

October 1, 2026
Cloned website images overlaid with phishing icons.

Organizational impersonation ranks as top online IP concern: with significant business impacts

October 1, 2026
AI resilience concept.

Survey highlights measures that organizations are considering for improved AI resilience

October 1, 2026
Fragility concept - a human head made up of jigsaw pieces starts to dissolve.

AI efficiency gains can increase organizational fragility

October 1, 2026
Advertisement
Resilience First
This week's most read articles
Open lorry car trunk full of moving cardboard boxes and furniture outdoors at city street.

HP Wolf study finds growing concern about attacks on hardware supply chains

August 6, 2024
A solar farm with associated wind turbines.

The resilience challenges of the renewable energy transition

October 2, 2026
Five stage crisis management framework

A five stage framework for a crisis management process

April 2, 2025
Latest resources
DRJ and BCI logos

DRJ and BCI publish guidance for governing, managing, and using AI in resilience

September 7, 2026
Load More

Subscribe to Updates

Get our Resilience Updates newsletter.

Most Popular Feature Articles
Three dark coloured light bulbs on a black background illustrate the concept of The Dark Triad in Crisis Management.

The Dark Triad in crisis management

Five stage crisis management framework

A five stage framework for a crisis management process

Blue interconnected gears and network nodes symbolizing automation and complex machinery.

Agent zero – the 2028 digital pandemic

Latest Reports
Global risks concept

UN report warns that the global risk landscape is being redrawn

Three blank wooden signs against a blue sky.

System restoration is not business continuity: research finds that ‘most cyber recovery plans are built for the wrong outcome’

BCI Continuity and Resilience Report 2026 cover.

BCI report sees growing structural divide between business continuity and resilience

A promo box for an article about resilience governance.
© 2026 Resilience Forward
  • About Resilience Forward
  • Newsletter
  • Newsfeed
  • Advertise
  • Call for Papers
  • Contact
  • Privacy Policy and Cookie Use
  • AI Use Policy

Type above and press Enter to search. Press Esc to cancel.

Manage Cookie Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behaviour or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}
Ad Blocker Enabled!
Ad Blocker Enabled!
Our website is made possible by displaying online advertisements to our visitors. Please support us by disabling your Ad Blocker.

Sign In or Register

Welcome Back!

Login to your account below.

Lost password?