By getting this mix of internal and external data right and using it to support more effective communications, CISOs can make the right decisions and get the support they need.

All the latest resilience and risk management news from around the world.
By getting this mix of internal and external data right and using it to support more effective communications, CISOs can make the right decisions and get the support they need.
The Enterprise Risk Management (ERM) Initiative at NC State University, in partnership with Protiviti, has released its 13th annual edition of the Executive Perspectives on Top Risks report.
A lack of consistent global AI standards is forcing enterprises to develop region-specific strategies, limiting AI scalability and benefits and creating future risks says Gartner.
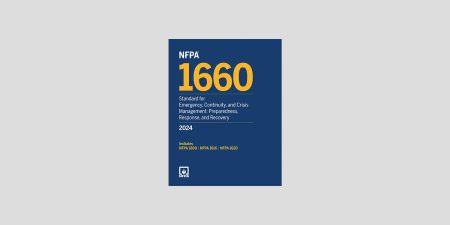
NFPA 1660 is the Standard for Emergency, Continuity, and Crisis Management: Preparedness, Response, and Recovery, which is managed by the US National Fire Protection Association (NFPA).
When organizations discuss business continuity, the conversation often focuses on plans, policies, and frameworks. While these are crucial enablers, they are not in themselves the point of business continuity.
GenAI and agentic AI security poses some unique challenges because we need to not only protect technology from being exploited by attackers but also from itself: there needs to be guardrails for the AI as well as protection against the AI.
While for most financial organizations DORA compliance has been an exercise built upon strong existing compliance, business continuity, and risk management processes, the focus on third party service providers in DORA could be a weak area. Andre Troskie explains why…
Following the COVID-19 pandemic work from home boom, the working world has generally embraced remote, flexible, and hybrid working options. In this article Caitlin Watkins provides 10 key steps that organizations can work through to achieve a secure remote workforce.
A load balancer acts as a traffic controller, providing exceptional performance and scalability for both on-premises and cloud application deployments.
The European Banking Authority (EBA) has announced that it has narrowed down the scope of its existing Guidelines on ICT and security risk management measures.